Drew Morana
Co-Founder, Whiten Baker. Forward-Deployed Engineer, Applied AI. A person who built a system that finds what vendors hide.
Of 4,121 security-relevant patches analyzed across nine ecosystems, 4,103 shipped with no CVE, no advisory and no notification. The fix went out. The warning never did.
99.6%Before the research.
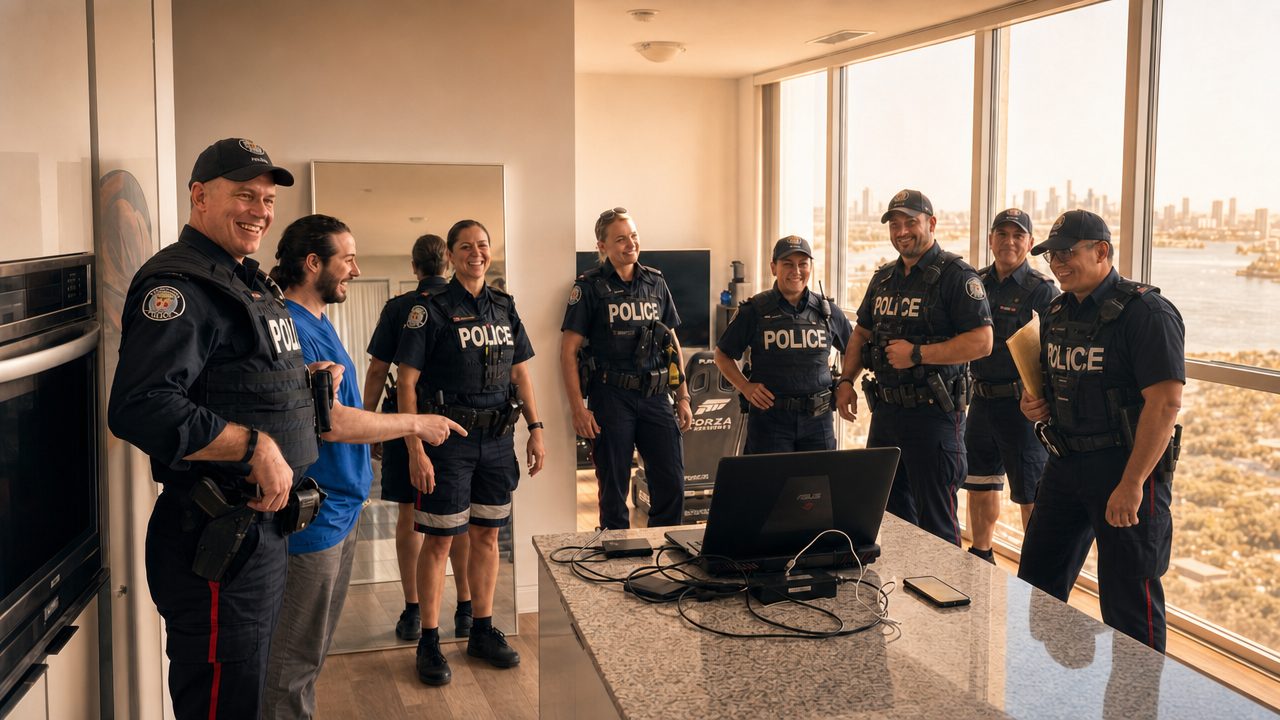
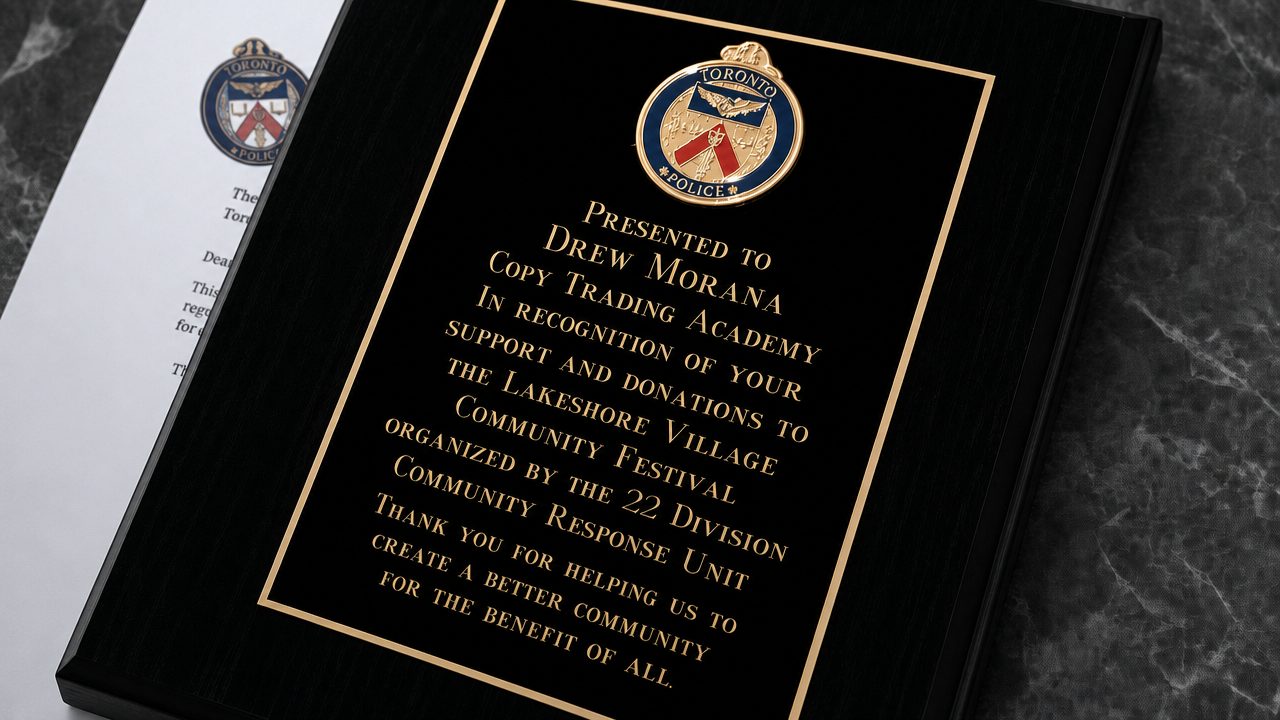
Community work with Toronto Police Service 22 Division. Funded community causes. Hosted events in underserved neighborhoods.
Lakeshore Village Community Festival · 22 Division Community Response Unit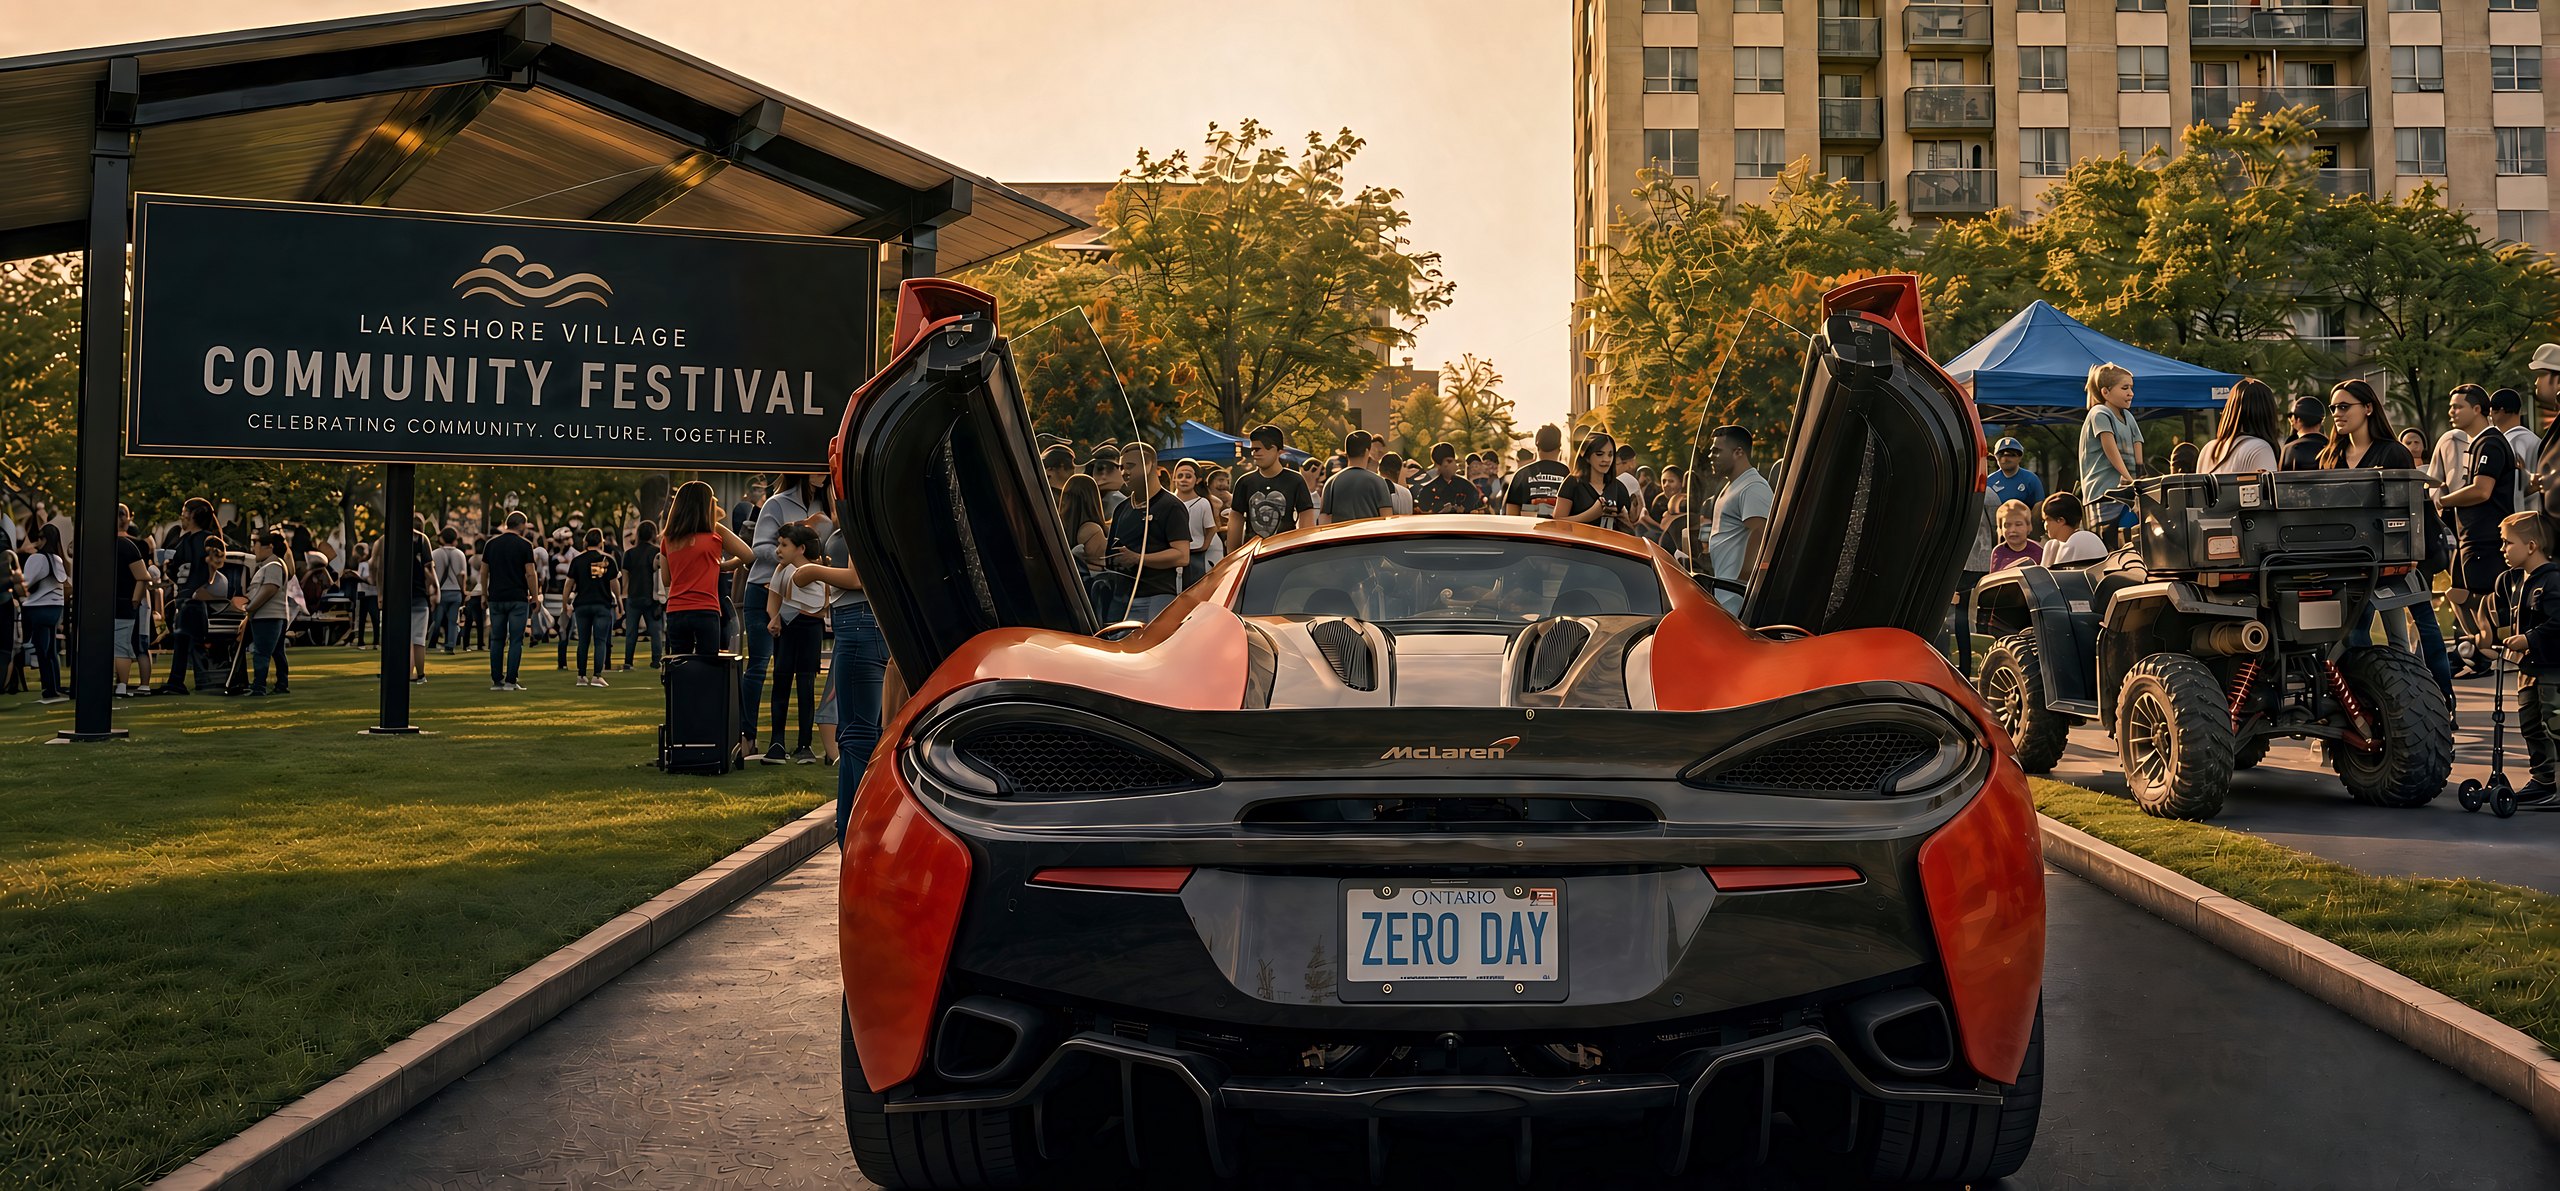
By the numbers.
MITRE records disclosed vulnerabilities. It cannot investigate the ones that are kept hidden. The gap was left to volunteers. We're one of them.
Verified researcher and Forward Deployed Engineer, Applied AI. 102 zero-days and climbing across Consensus, Secrets, and Authentication Infrastructure. We do not name the vendor. We protect them.
The research is the foundation. Before the tooling, before the regulatory work, the question is always the same: can the bug be reproduced, and does the impact survive cross examination. Nothing leaves the bench until it can.
- CVE-2026-37171, assigned by MITRE. More submitted and awaiting review.
- 102 zero-days across Consensus, Secrets, and Authentication Infrastructure, and counting
- Documented vendor misconduct across nine-plus vendors: theft of findings, silent patching, evidence concealment
- The only systematic measurement of vendor disclosure compliance run at this scale by an independent firm
- Active regulatory filing with the Ontario Securities Commission
The Standard
Every finding undergoes a structured kill-loop with forced negative confirmation before submission. If it cannot be exploited, it is not a finding. If a triager would close it Informative, it is not a finding. Only what survives reaches the public record.
The tooling.
Three instruments built for the work no off-the-shelf platform was designed to do. The first sweep analyzed 4,121 patches across nine targets in under ten minutes.
Detection at scale is the multiplier. A single researcher reading commits cannot find concealed patches across nine major projects in any reasonable timeframe. With the right instrumentation, the same researcher can do it in minutes and surface findings that human review would miss for years.
Ghost Patch Scanner
Detects silently patched security vulnerabilities at scale. Thirty-plus security signatures, NVD cross-reference, and automatic CVE draft generation.
Cascade Engine
Maps how a single vulnerability propagates across every fork, dependency, and downstream deployment. Generates disclosure notices and MITRE supplements automatically.
Fork Drift Analyzer
Identifies where a fork has diverged from upstream security patches and quantifies the exposure window. First run flagged 13 forks. All 13 vulnerable. Zero patched.
Where The Tools Live
These instruments do not exist anywhere else. They were built specifically for the work of detecting concealed disclosure failure at scale, and they remain proprietary to the firm's research engagements.
We designed and built a seven-layer scaffolding framework on top of Claude Code that turns a general-purpose coding agent into a disciplined, evidence-first vulnerability hunter. Built solo. In house.
Kill-loops with forced negative confirmation. Multi-pass hunting in isolated sessions. MCP tool integration spanning Semgrep, CodeQL, and sandbox execution. Orchestrator-pattern subagents. Persistent cross-session memory. Autonomous run loops with thirty-minute anti-wandering checkpoints. The model is not the moat. The system is.
Five of the seven layers were independently validated when Trail of Bits productized the same architecture in their public skills library. A solo researcher with aggressive scaffolding on a niche target out-finds a large team optimizing for breadth, because depth beats coverage when the target is neglected.
The Reference
Published reference document available on request: The Scaffolding Tax. Maps every layer of the framework against the Trail of Bits productized equivalents.
Where the teeth are.
The hallway between a finding and accountability is long. We walk it. Every filing, every regulator briefing, every expert testimony, begins here.
Everyone running the code gets notified of an available update. A CVE is one way to carry it. An alert from the creator continues building trust.
Ontario Securities Commission · MITRE CVE Authority · Expert TestimonyMost researchers talk to developers.
We talk to regulators.
That Is Where The Teeth AreWe honor what a warrant canary stands for. We believe you have the right to be protected by one.
Get in touch.
Drew Morana
For confidential briefings, regulatory cooperation, expert advisory, and media on the record.
drew@whitenbaker.comThe Firm
For engagement requests, vendor accountability submissions, and routine correspondence.
info@whitenbaker.com